
SSHepherd ®
STEALTH MODE SECURITY
What cannot be found, cannot be exploited
External hackers and internal rogue employees discover critical on-premise and cloud server assets by scanning for open, listening ports.
SSHepherd® provides secure, controlled access to these servers while the ports are closed. This is not obfuscation, redirection, or port knocking. The ports are closed, completely off. As a result, the attack surface does not exist and there is no service for adversaries to exploit.
What are the implications?
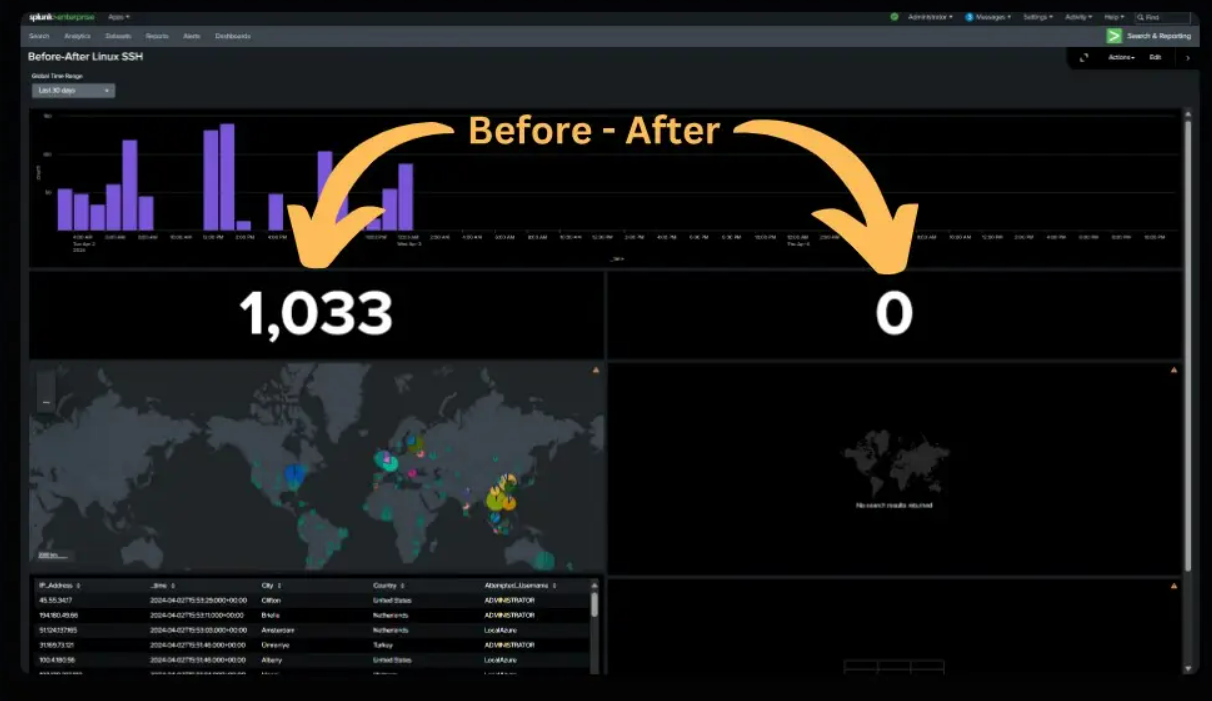
From thousands of potential attack vectors to absolute zero
See the Difference
SSHepherd® Use Cases
See SSHepherd® in action
WATCH THE DEMO
Watch how SSHepherd closes every listening port on a live server — SSH, RDP, and application ports — while authorized users retain full, uninterrupted access. See the attack surface disappear in real time.
How SSHepherd® was born
REMOVE THE ATTACK SURFACE
SSHepherd® completely removes the open, listening ports for SSH, RDP, and applications like databases while still maintaining the full access and functionality of those services and applications.
Make Your Servers Invisible Today
Secure your infrastructure before threats can find it
On-premise, cloud, physical and virtual servers
Patented technology
Zero Trust containment to authorized users only
Quick 10-minute setup